Developers
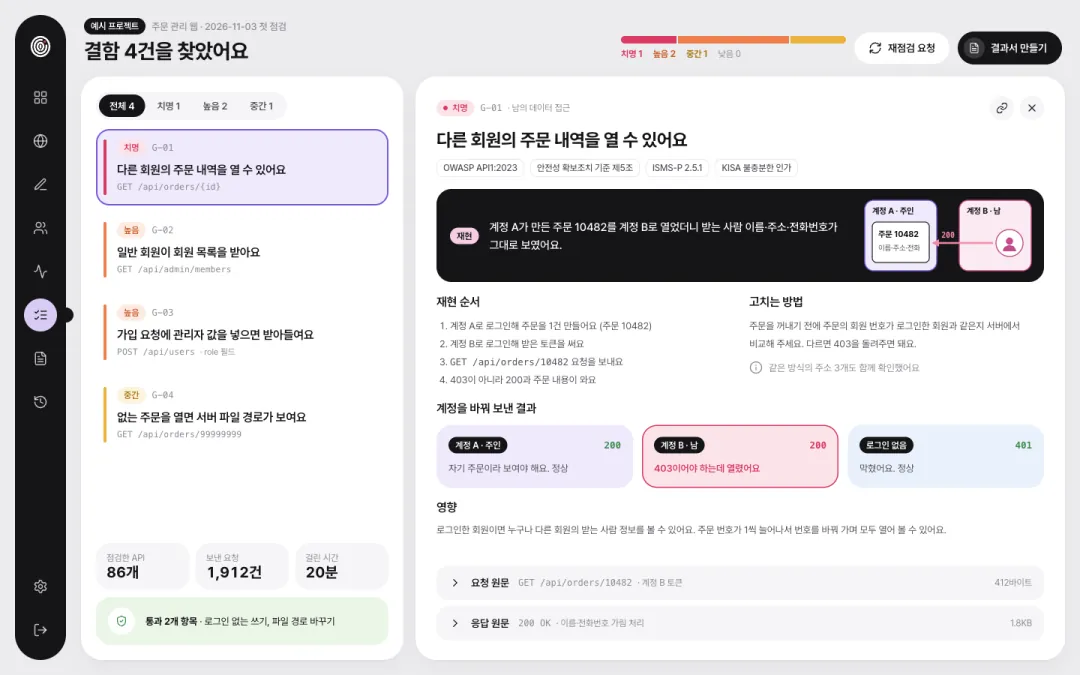
Results screen
For each flaw: reproduction steps, response comparison per account, and raw requests and responses. Personal data in responses is masked.
We swap requests between 2-3 test accounts to test 6 kinds of authorization flaws. Results come as a report with reproduction steps and fixes.
Product name gate · gate.define404.com · Beta
01Test categories
Each category carries its standard reference numbers. The same numbers appear in the report's standards mapping.
Account B sends read and update requests using an order number created by Account A. If it opens and A's values show, that's a flaw.
What we send
GET /api/orders/10482We call routes seen only from the admin account using a regular member's token. If a response comes back, that's a flaw.
What we send
GET /api/admin/membersWe slip values like role and is_admin into sign-up and update requests, then read the record back. If the value changed, that's a flaw.
What we send
POST /api/users {"role":"admin"}We call write routes without signing in. If they aren't blocked, that's a flaw. Off by default and enabled only on test URLs.
What we send
POST /api/orders (no token)We put ../ or another user's file number into download paths. If a file comes down, that's a flaw.
What we send
GET /api/files/../other-user.pdfWe send requests for nonexistent resources and invalid values. A 500 error or a visible server path or stack trace is a flaw.
What we send
GET /api/orders/9999999902How you get results
The same results, shown three ways for three kinds of readers.
Developers
For each flaw: reproduction steps, response comparison per account, and raw requests and responses. Personal data in responses is masked.
Whole team
A PDF and web view with a cover, counts by severity, a flaw index, a chapter per flaw, and the standards mapping.
Commissioning company
Shows only pass or fail per category and the last test time, no sign-in needed. You can turn it off anytime.
03Retest
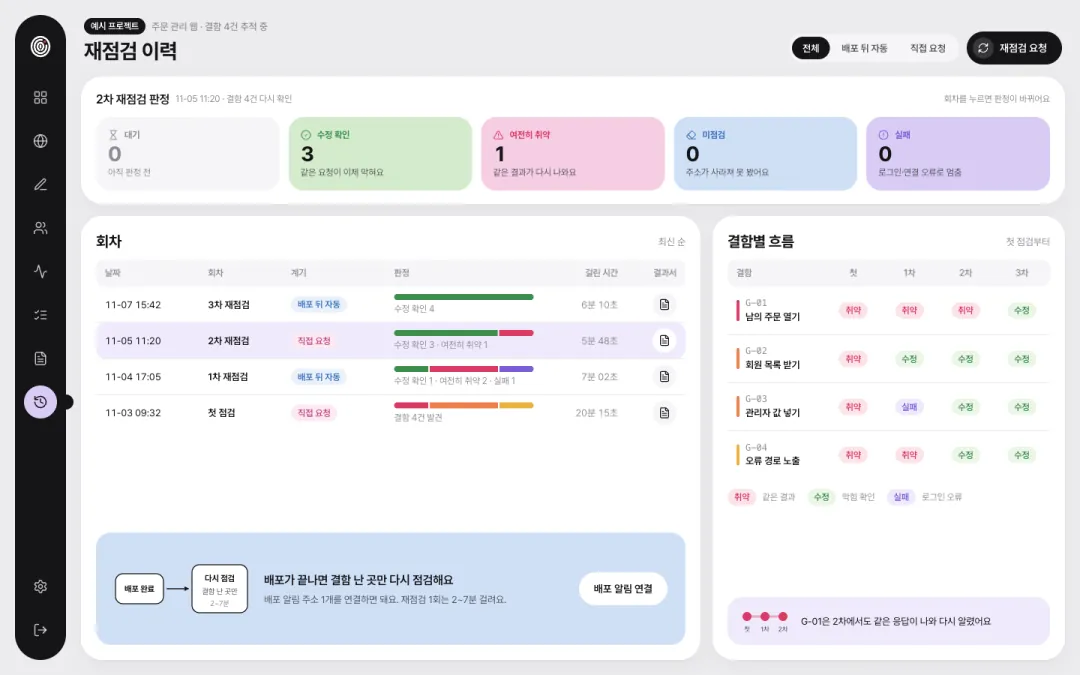
There are five verdicts: Fixed, Still vulnerable, Not tested, Failed, and Pending. History is kept for every run.